About
AI produces probabilities. The systems it acts on, such as payment rails, databases, legal deadlines and servers, need certainty. QWED puts an exact check between the two, in the open, so anyone can see how a verdict was reached.
What QWED is
QWED is open-source runtime verification for AI output and agent actions. It checks the numbers, rules and actions in AI output with exact methods, before anything executes. Only what it can prove is admitted; everything else is denied by default, and your systems act on that decision.
It is a platform on one verification core: open-source packages for finance, legal, tax and cloud infrastructure; checks for AI agents and the protocols they use; tools that run in your code and on your servers; and one GitHub App, QWED Security.
See the whole platform- 9open-source packages
- 22security advisories published openly
- 14contributors so far
- Apache-2.0licence for the code
Principles
-
Exact checks first
Use a solver, parser or rule wherever one exists. The model translates; it does not decide.
-
Fail closed
If a claim cannot be proven, it does not pass. Silence is never treated as approval.
-
Evidence with every verdict
A result that cannot be audited later is not a verification.
-
Open by default
The code, the specs and every security advisory are public.
Who builds it
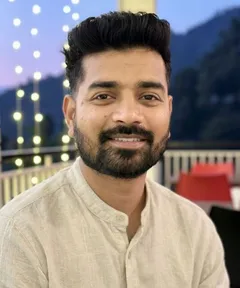
Rahul Dass
Founder and maintainer
QWED is founded and maintained by Rahul Dass. Decisions follow a written governance model, and contributions from the community are welcome in every repository. 14 people have contributed so far, and each one is credited on GitHub.
If the maintainer is unavailable
QWED has one maintainer. That is a real risk for anything built on it, so here is what exists today and what does not.
-
Everything is public
Code, specifications, documentation and every security advisory, under Apache-2.0. Anyone can fork QWED and keep running and maintaining it without asking, and 14 people have already contributed code or security reports. Contributors
-
Releases come from CI
Packages are published through PyPI Trusted Publishing, with build provenance attestations, not from a personal machine. How releases are protected
-
Access is protected
Two-factor authentication is enforced for the whole QWED-AI organisation on GitHub, and required for anyone with write access to PyPI or Docker Hub.
-
Decisions are written down
Roles, how decisions are made and how access is granted are set out in the governance model. Governance
Not in place yet
No backup maintainer with administrative access has been appointed. When one is, they will be named in the governance model, with what they can do if the maintainer is unavailable for more than four weeks.
Supported by these companies’ programs for open-source projects and startups
They give QWED free access to their products.
 Docker
 Cloudflare
 Sentry
 CircleCI
 Buildkite
 Mintlify
 Sanity
 Heroku
 Atlassian
 Greptile
- Docker
- Cloudflare
- Sentry
- CircleCI
- Buildkite
- Mintlify
- Sanity
- Heroku
- Atlassian
- Greptile